Discover the highlights of KubeCon 2024: the advent of artificial intelligence, WebAssembly in the Cloud Native universe, developments in the Supply Chain, the latest trends in security and sustainability, as well as the constant evolution of Kubernetes . A look at the technology maturity and forward thinking shaping the future of the cloud.
Discover how to secure your AKS (Azure Kubernetes Service) secrets in a KeyVault using Workload Identities.
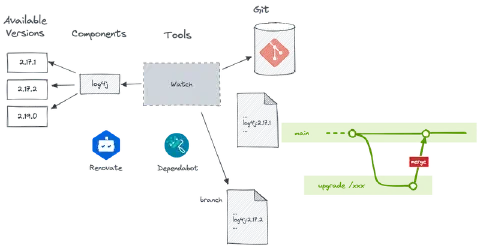
In this series on Supply Chain Attacks, let’s focus on the importance of updating your dependencies, a crucial step for the security and maintainability of your applications.
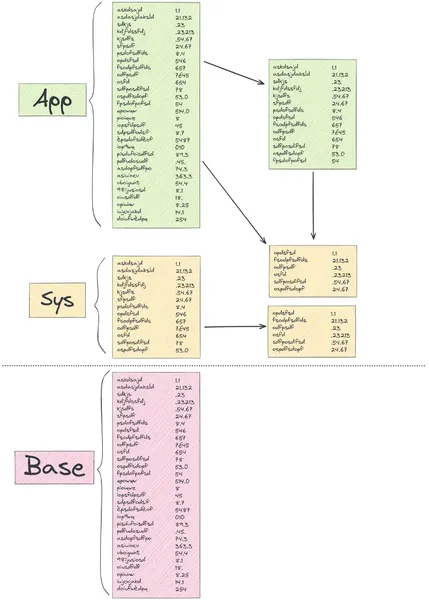
Why publishing a Software Bill of Materials (SBOM) matters for Supply Chain security, and how to generate, standardize and consolidate it across your CI/CD and container images.
What a Supply Chain Attack is, its real world impacts, and the DevSecOps best practices and CI/CD safeguards that help protect your software delivery pipeline against it.