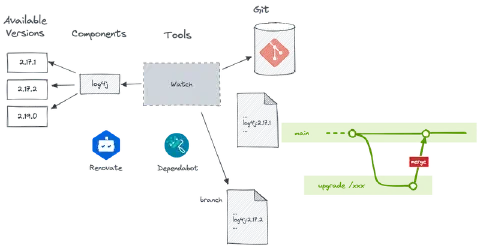
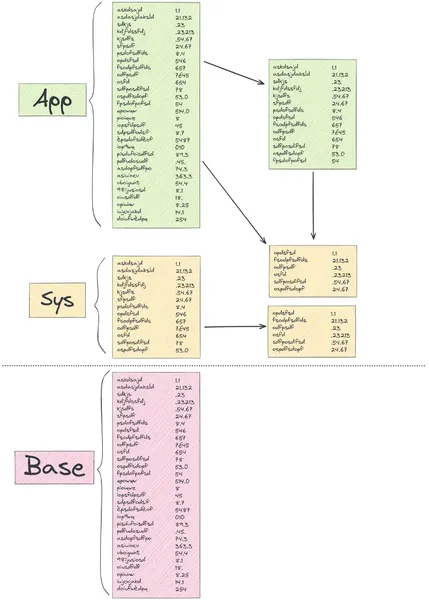
In this series on Supply Chain Attacks, let’s focus on the importance of updating your dependencies, a crucial step for the security and maintainability of your applications.
Why publishing a Software Bill of Materials (SBOM) matters for Supply Chain security, and how to generate, standardize and consolidate it across your CI/CD and container images.
What a Supply Chain Attack is, its real world impacts, and the DevSecOps best practices and CI/CD safeguards that help protect your software delivery pipeline against it.
A comparison of lightweight Kubernetes GitOps secrets management solutions, Bitnami Sealed Secrets and Kamus, covering encryption, decryption, installation and real world usage.